Draft of Scoping Decision Tree
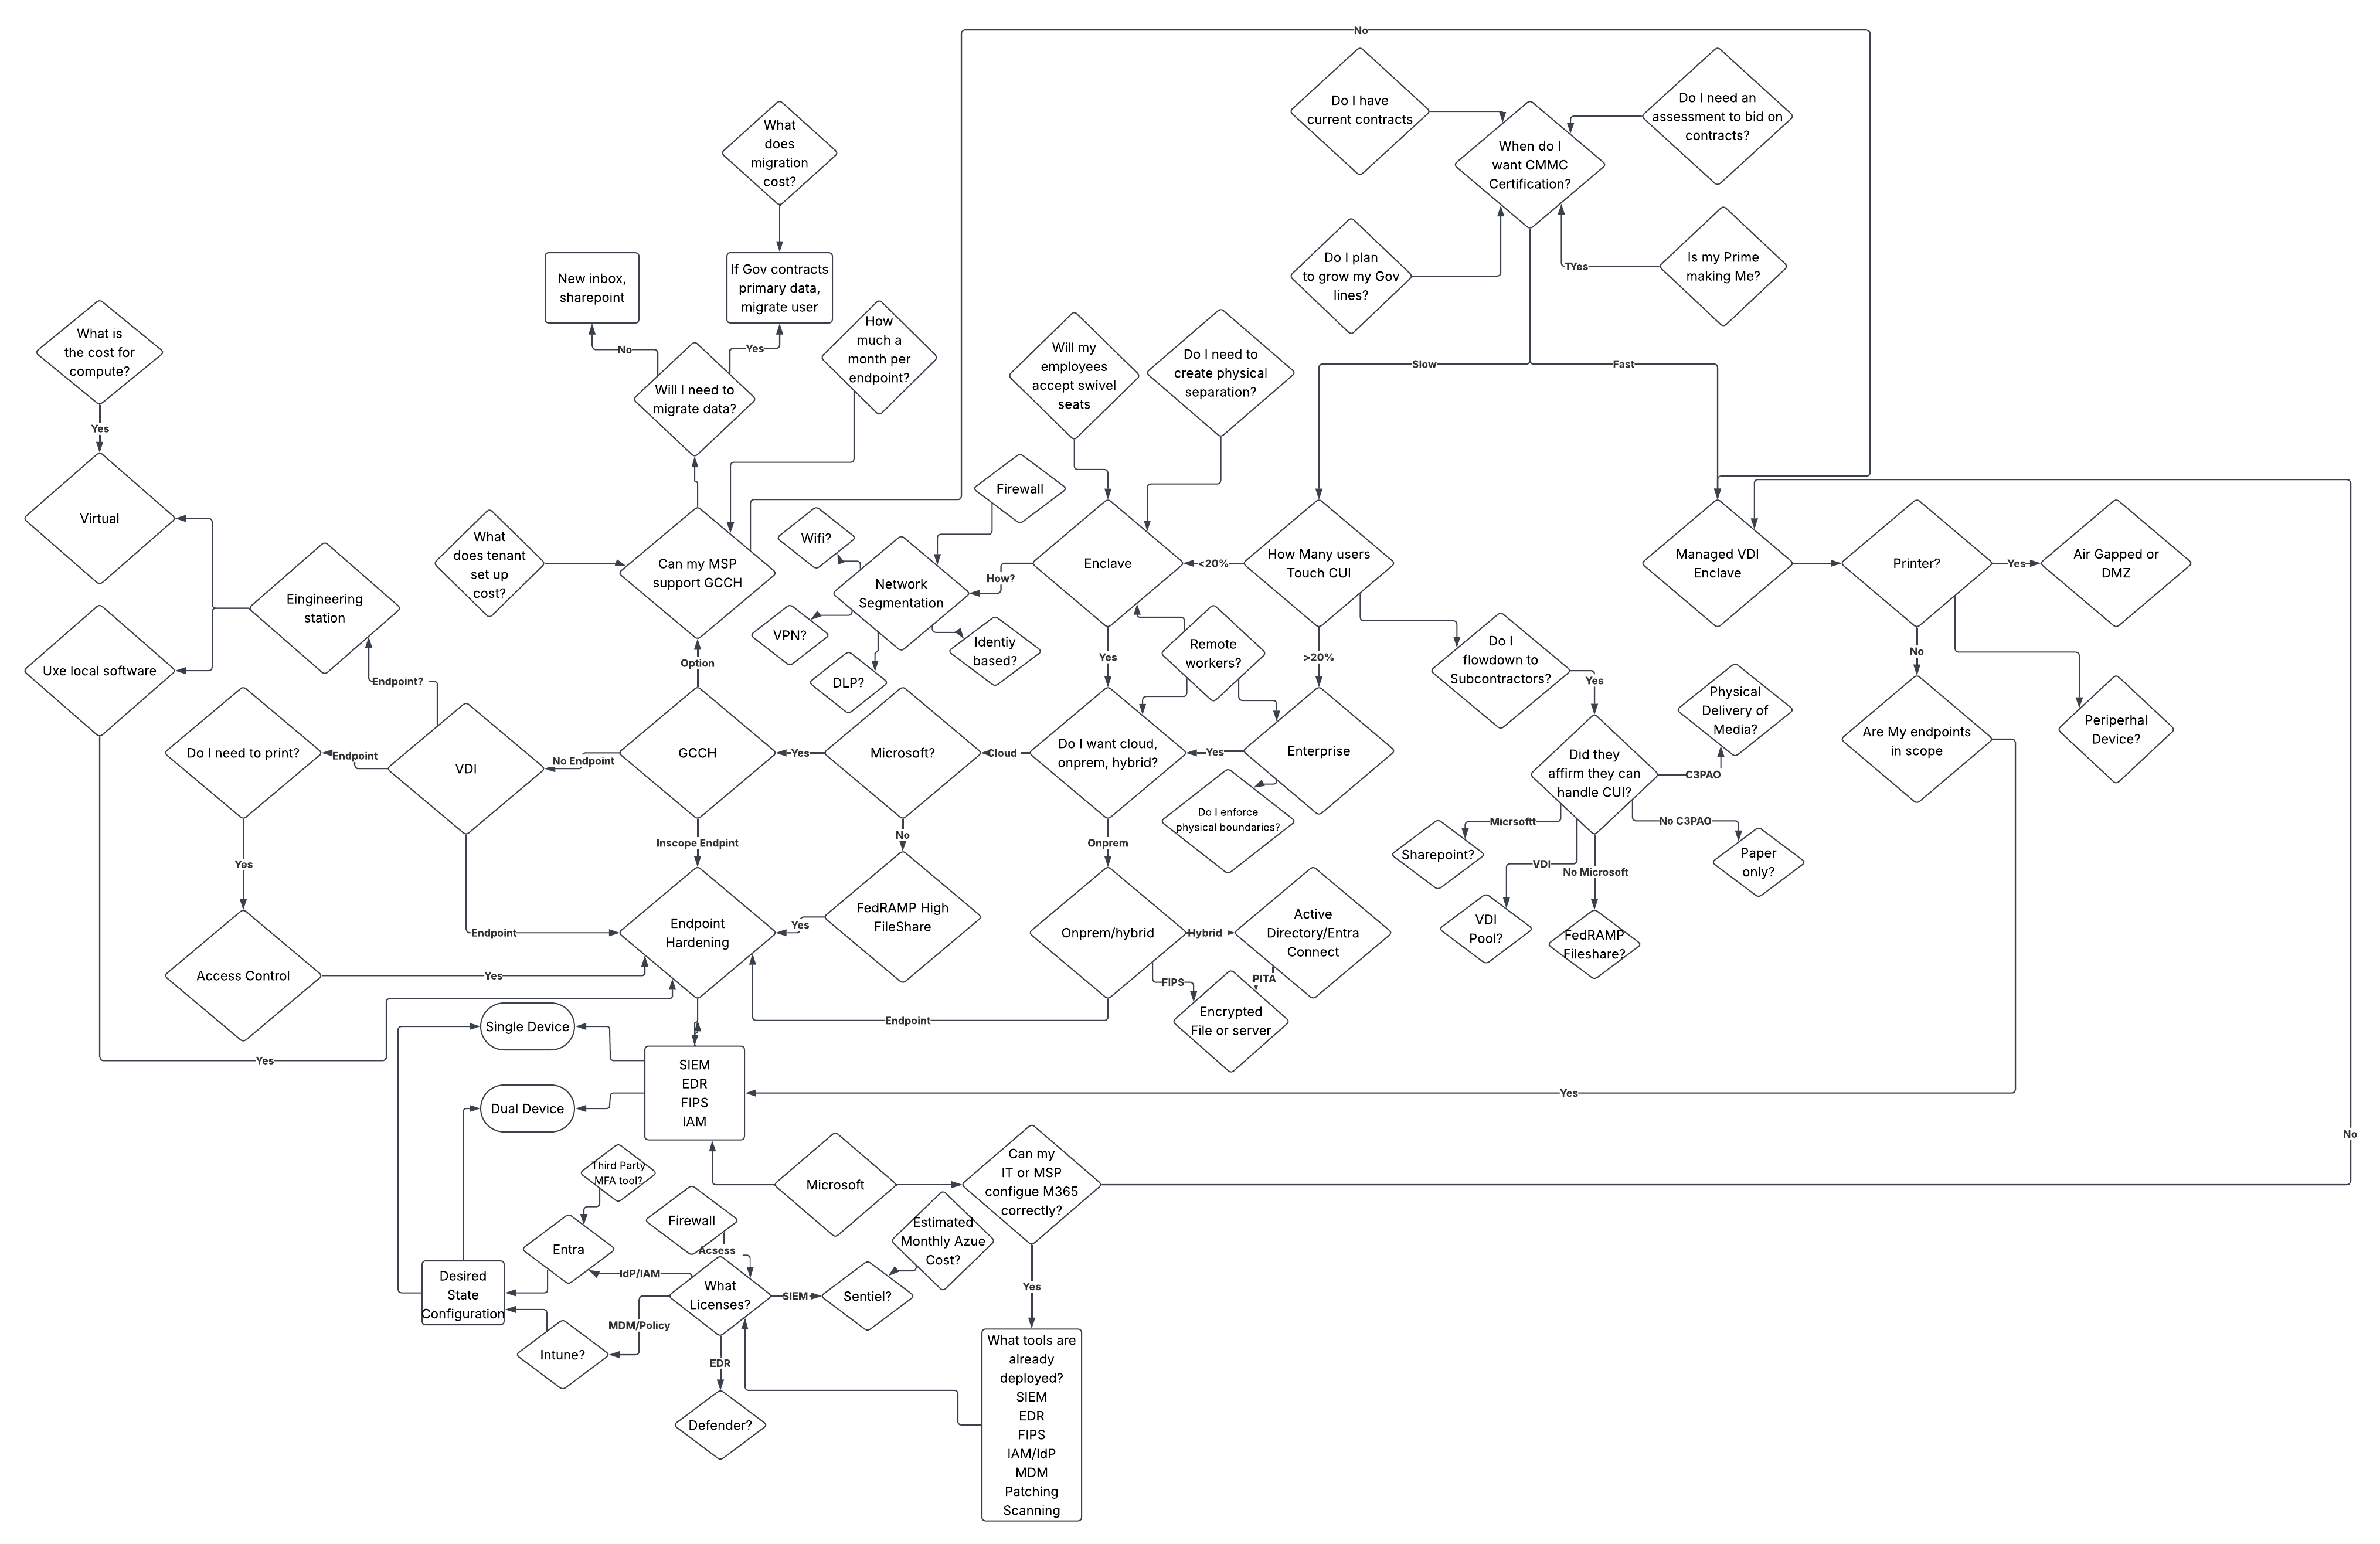
Draft of Scoping Decision Tree
Folks often bemoan compliance or security as paperwork and checkbox exercises, but that misses the point of Document Control. Policies, plans, and procedures exist to ensure your business does work in ways that meet laws and regulations. They also exist to describe how you get …
alright @manton still no web ring plug-in…we gotta find a community member to fix that.
In terms of CMMC many organization feel overwhelmed by documentation and do not always understand the distinction between policy, plans, and procedure. Yet we often get lost in the effort to meet compliance requirements and forget that the “G” in GRC stands for …
Do all NIST-SP-800-171 requirements need continuous monitoring? Which ones are annual? Which controls are monthly? Weekly? Right now an organization seeking CMMC certification can decide on which requirements get met by controls that need a defined cadence. As you make these …
A lot of organization who rely on Mobile Device Management are starting to understand the risks of Bring Your Own Device. Watching the Stryker Incident where Intune erased personal devices managed by employers has put the issue in stark contrast. Mobile Device Management is not …
Big Announcement
The DIB CS Program is OPEN for new companies. The outreach and onboarding functions have transitioned to DC3.
DIB Companies, with or without an FCL, working with CUI, can apply at DC3.DIB.CSRegistration@us.af.mil
Proud to Announce CyberDI’s Awareness and Training Programs to meet your CMMC requirements and improving a culture of security CyberDI Awareness and Training Program
Why do back ups live in the Media Protection family? Ransomware threatens your business everyday, and backups help to inoculate your systems. Why do back ups get such a small mention in NIST.SP.800-171r2? NIST explains in NIST-SP-800-171r2 they pulled “CP-9, System Backup” into …
AI For Security S ecurity For AI
A good intro to the risks, challenges, and opportunities
Many people are confused by the Cross tenant collaboration and the new Microsoft UX:
gcch-m365-webinar-connect-collaborate-create-june-2025-complete.pdf
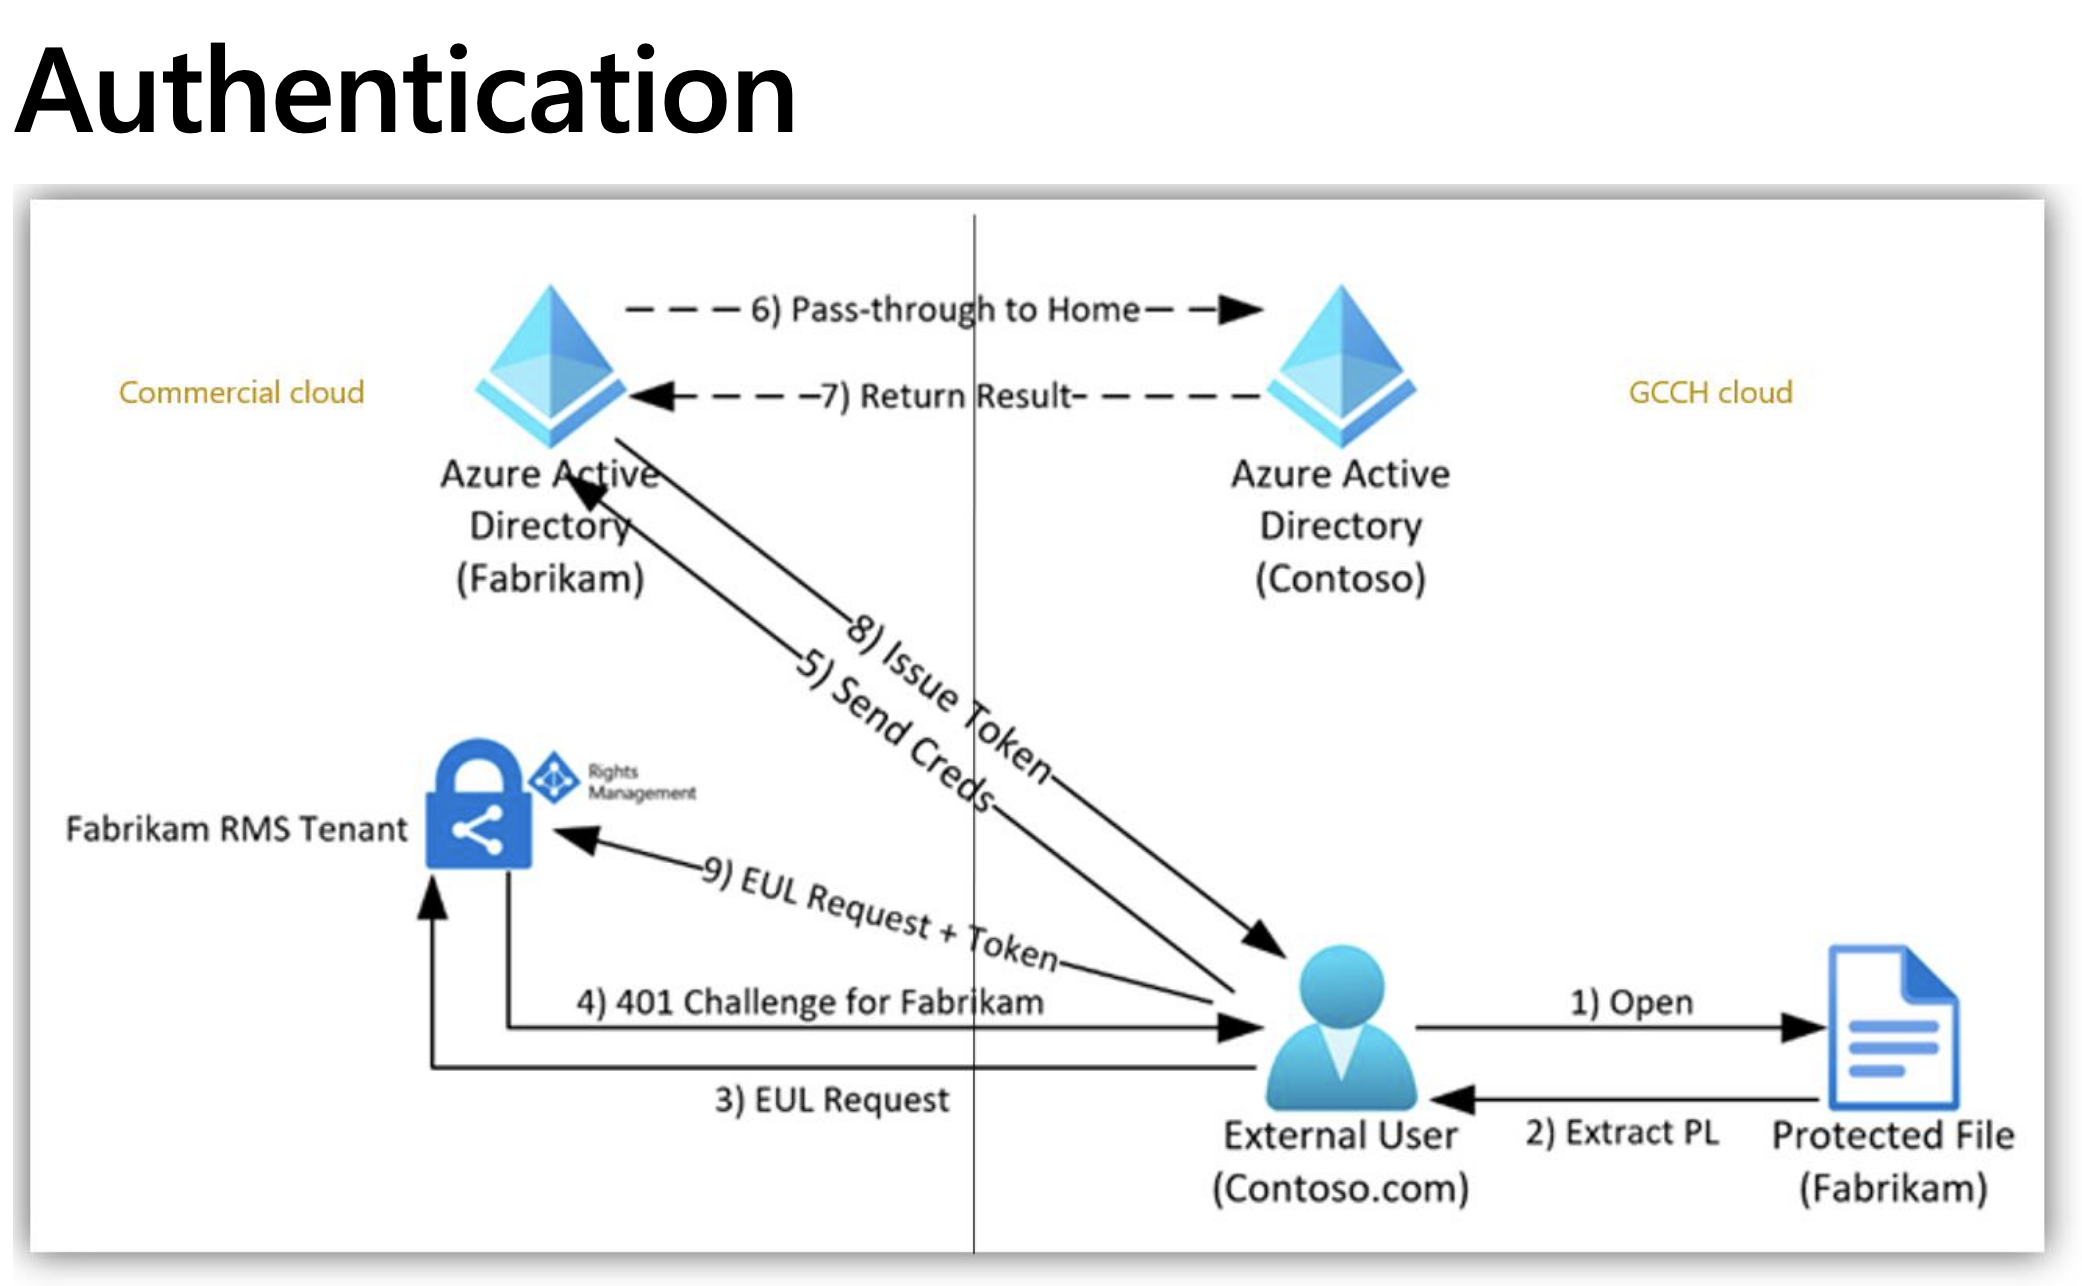
Adding sensitivity labels to SharePoint: learn.microsoft.com/en-us/pur…
unlabeled filed continue to be protected with current SharePoint permissions for the user, even though the files have left original SharePoint boundary
COOL!
Adding cross posting to Blue Sky
People keep asking, “What they can do?”
How can they help
If you are a small business owner one of the best things you can do is make sure you have a good backup and recovery plan
Good back ups are the Victory Gardens of the 21st Century
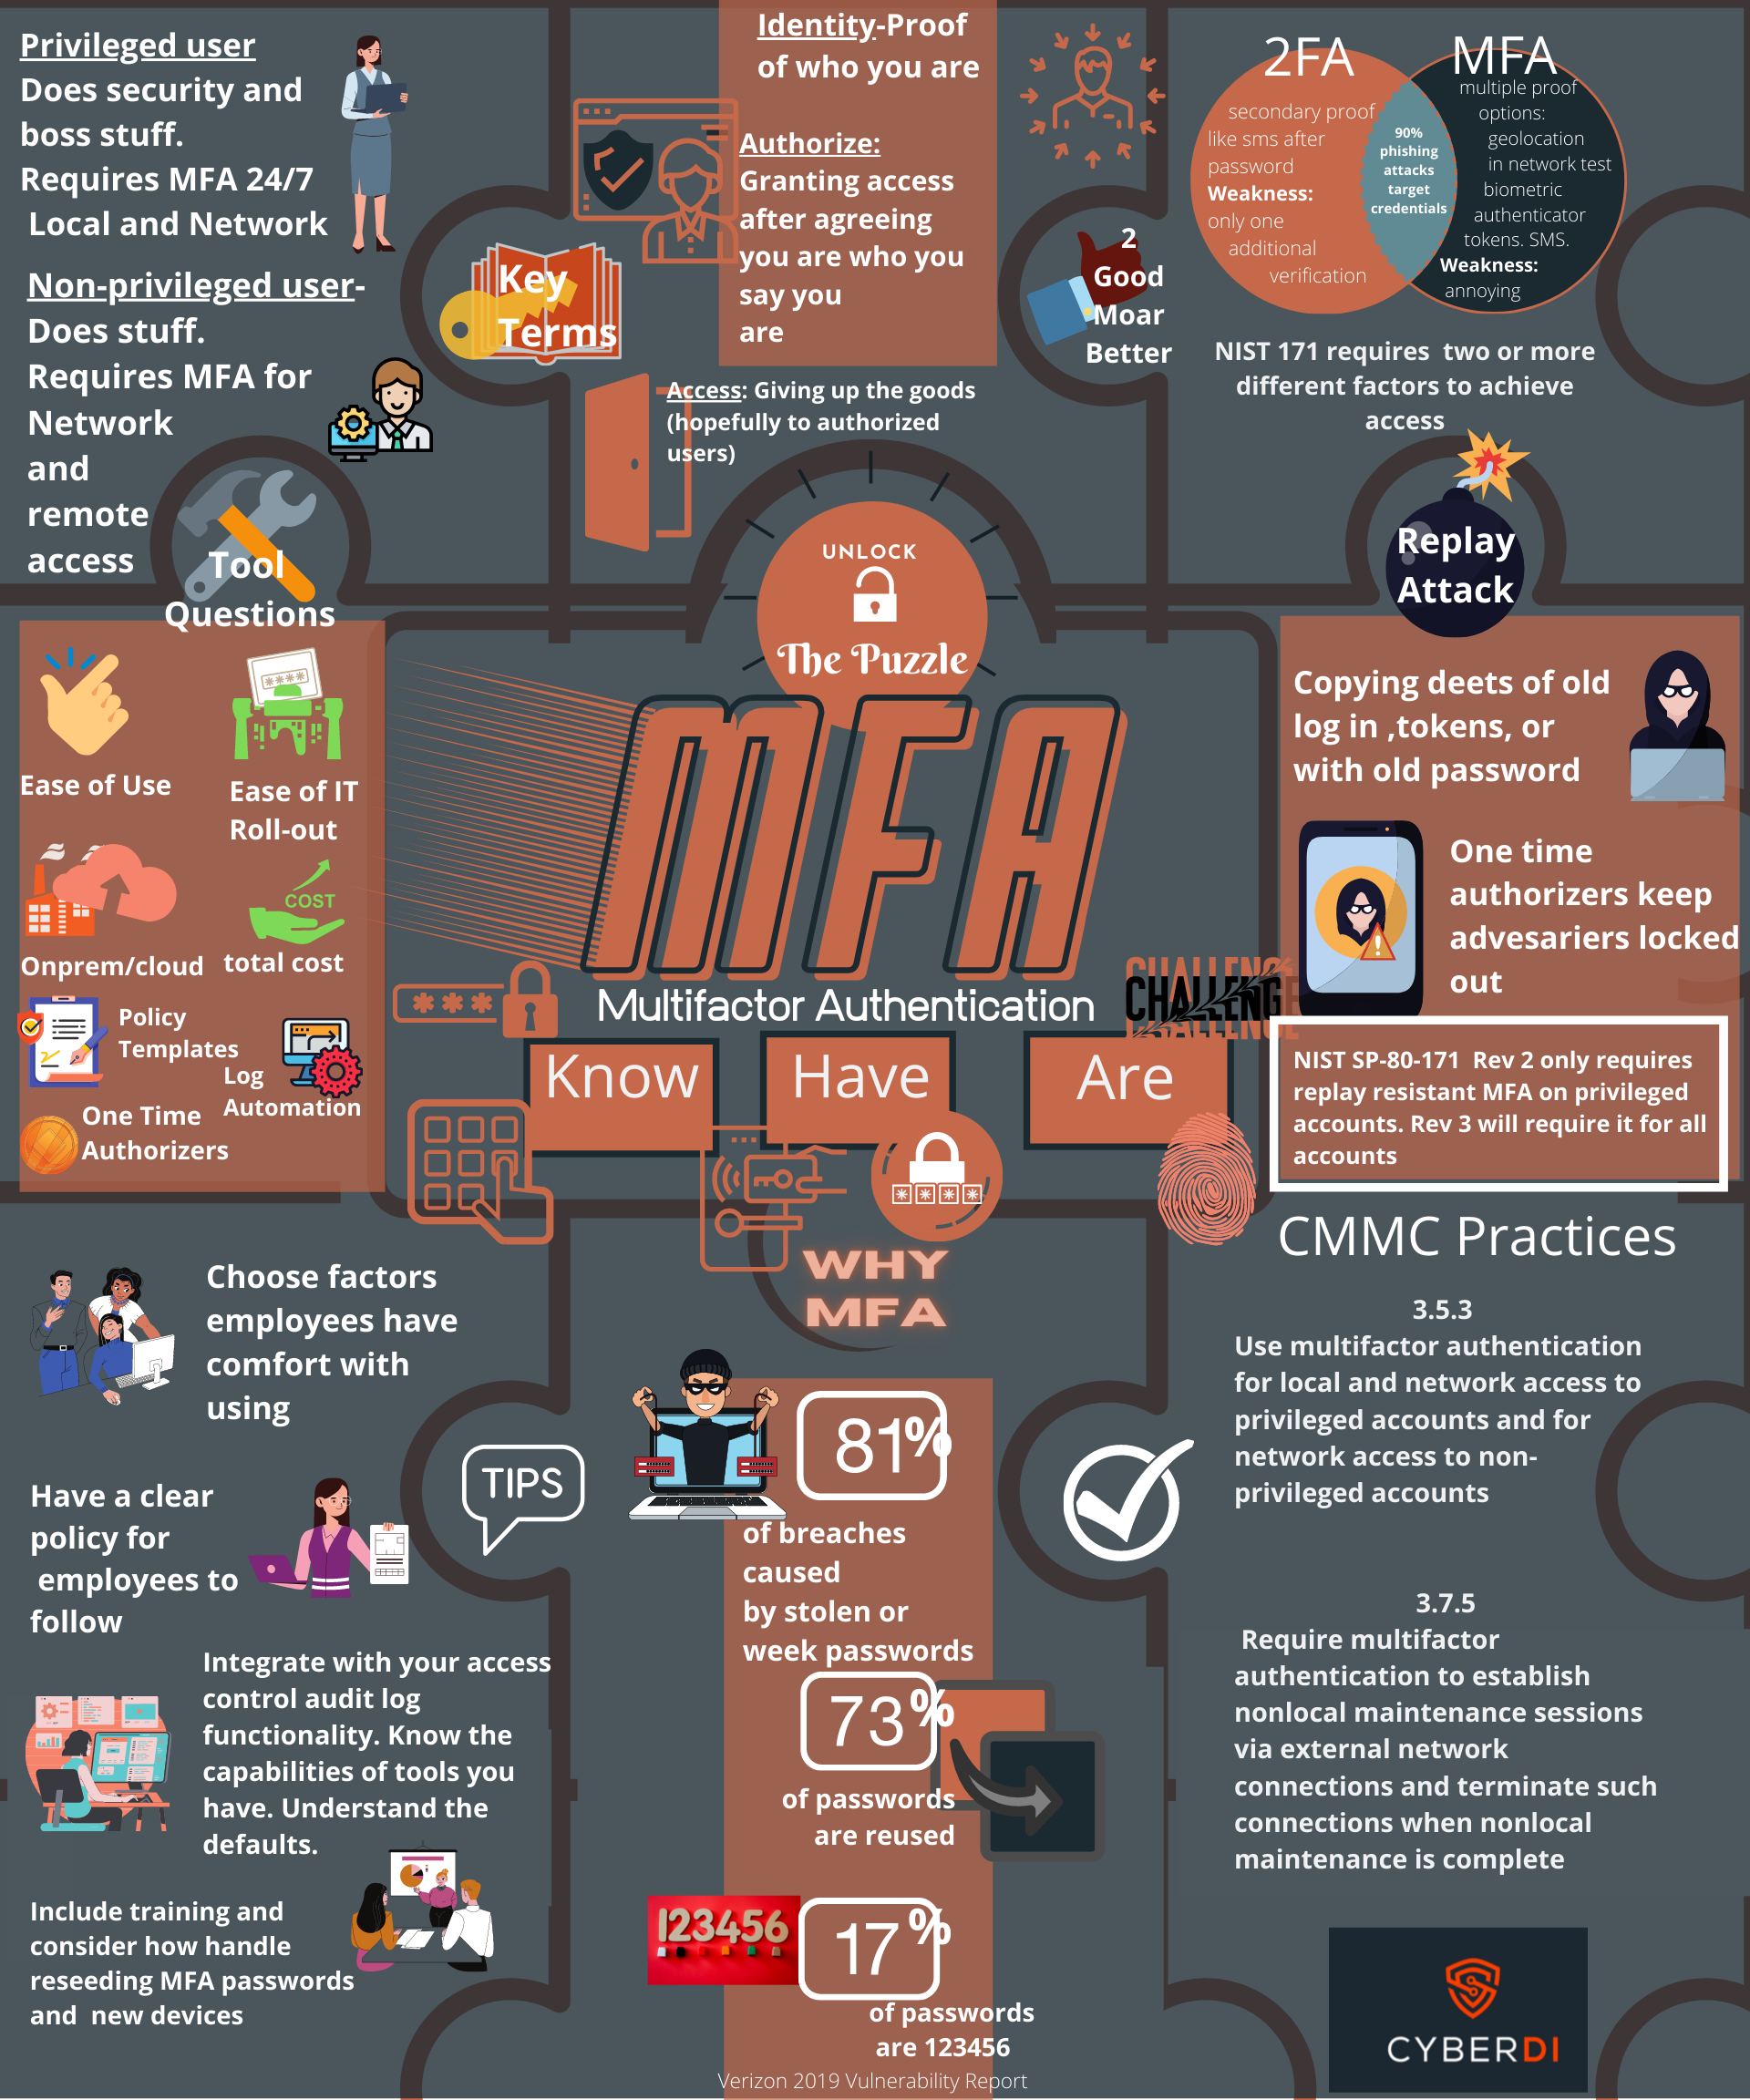
Many companies are now hearing more and more about Multi-Factor Authentication. In fact for most small businesses you can no longer get insurance, let alone cyber coverage, without ensuring MFA gets used for all sensitive data.
Really if you can turn on Multi-Factor Authentication. You should
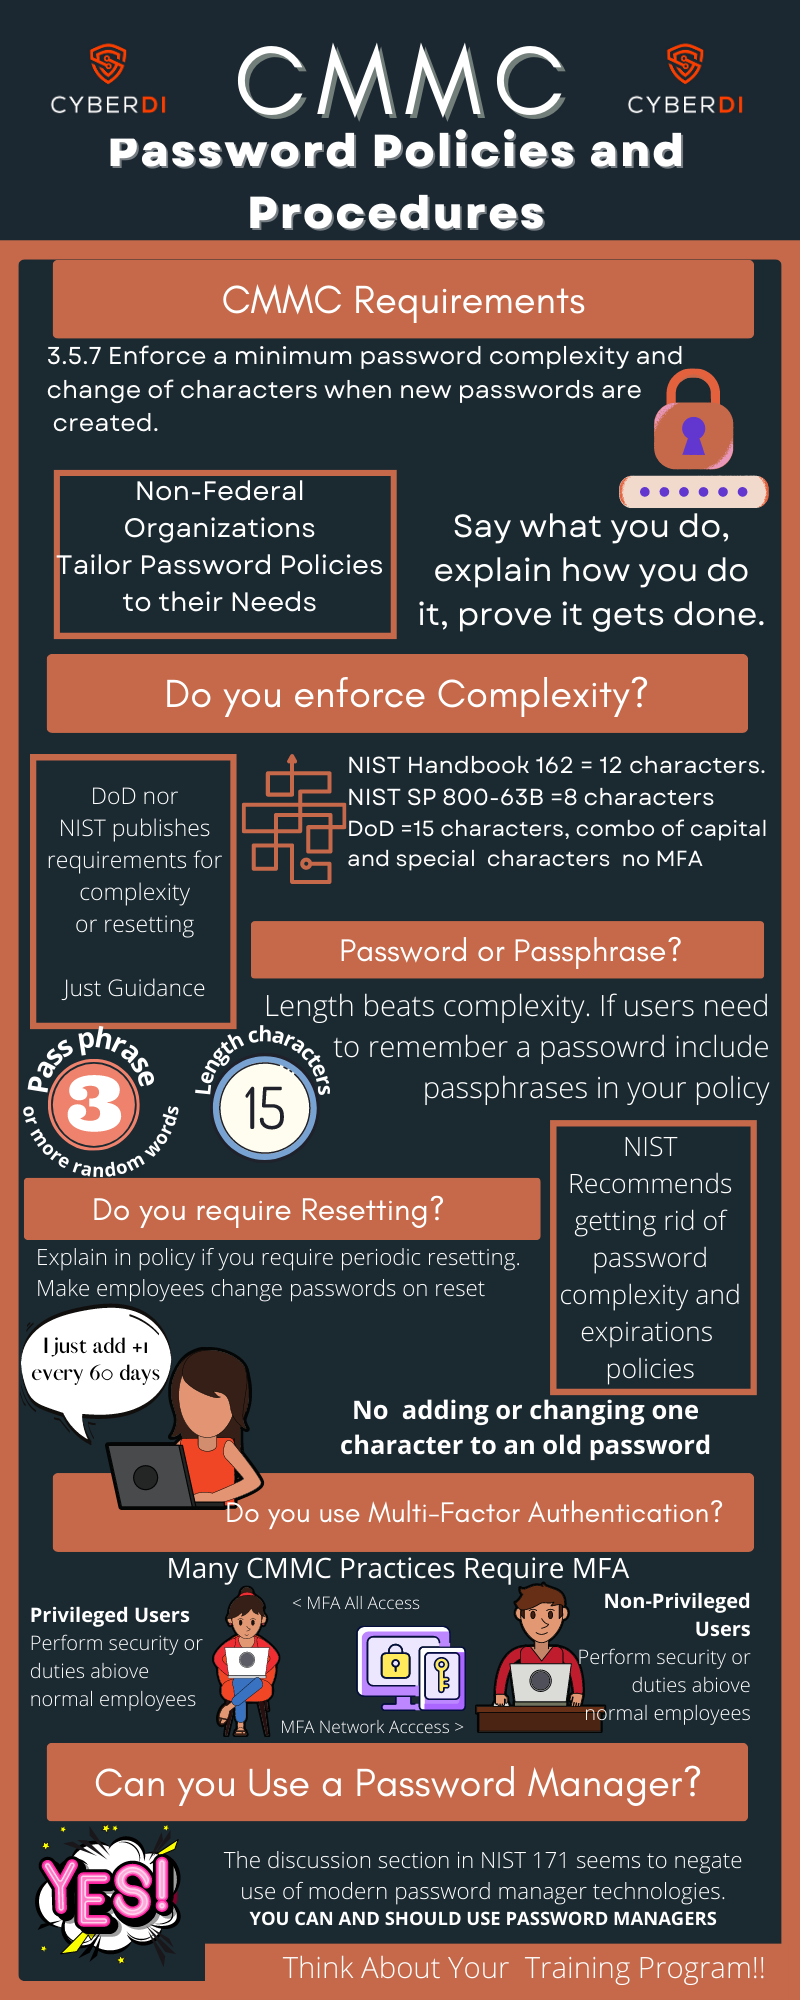
Certified CMMC Assessors click into place as just another cog in a much larger system that already exists. Every objective that a CCA examines must already be legally met by Organization Seeking Certification. CMMC introduced no new requirements on Federal contractors. When …
Hanging at Converge Security and learning about Conway’s Law at the Keynote addresds